AegisSOC — Autonomous Cloud Defense & Zero-Day Threat Hunting Radar
Distributed real-time cybersecurity SIEM and autonomous SOAR pipeline ingesting 120,000 events/second with automated exploit isolation.
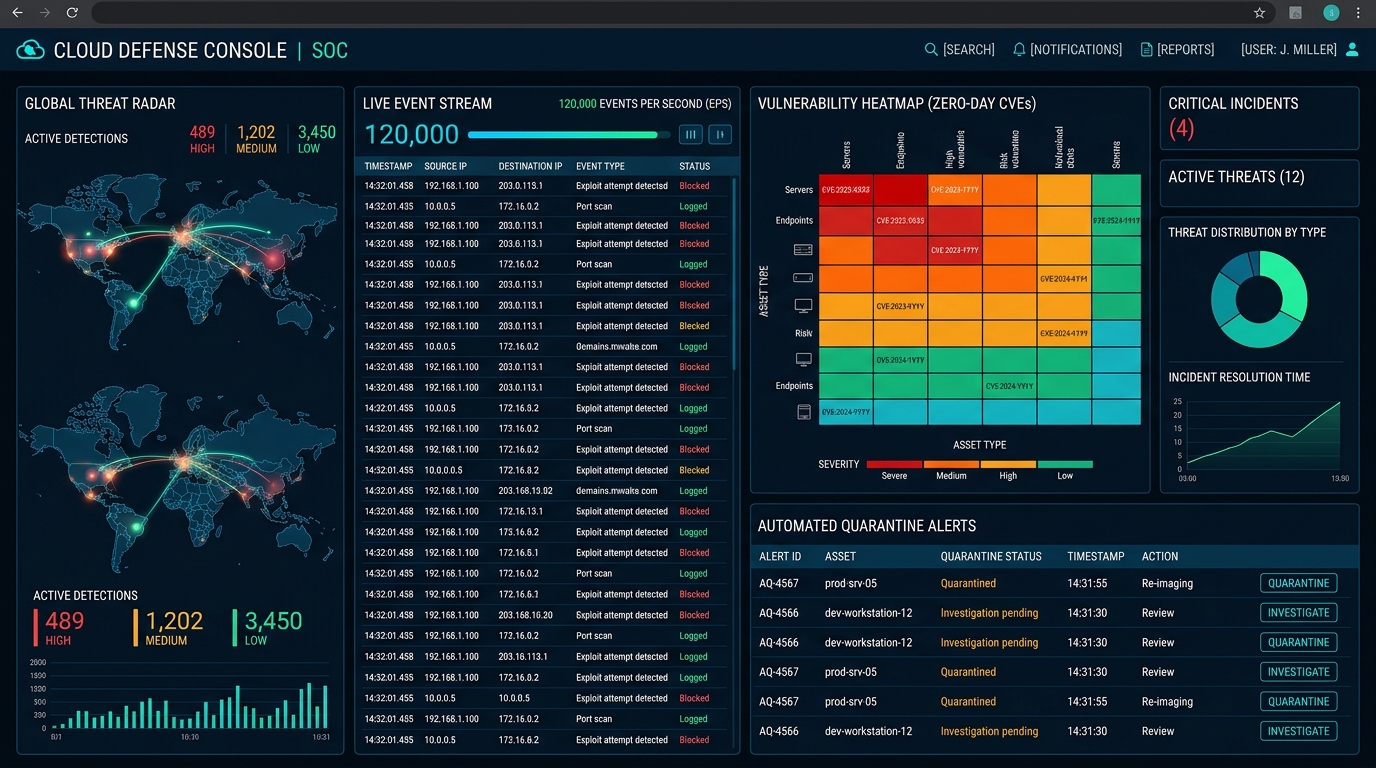
Events per second (EPS) ingested and evaluated in real-time
Mean time to detect and quarantine zero-day threats
Multi-stage behavioral anomaly filtering rate
SOC 2 Type II, ISO 27001, and NIST compliance telemetry
Project Overview
AltosForge architected and engineered AegisSOC, a next-generation security operations console and autonomous incident response platform. By unifying eBPF kernel telemetry, distributed ClickHouse log streaming, and graph anomaly detection, AegisSOC isolates zero-day exploits and credential stuffing campaigns in under 4 minutes across multi-cloud environments.
Crippling Alert Fatigue and Slow Incident Quarantine Times
Security analysts were flooded with over 45,000 daily alerts from fragmented legacy SIEM tools, obscuring genuine zero-day threats.
Mean time to identify and contain compromised cloud instances averaged 3.5 hours, leaving perimeters vulnerable to lateral movement.
Multi-cloud Kubernetes clusters (AWS EKS, Google GKE, and Azure AKS) lacked centralized network packet observability.
Manual compliance auditing required weeks of tedious log aggregation before annual SOC 2 inspections.
Kernel eBPF Telemetry with Distributed ClickHouse and Automated SOAR Playbooks
We built a high-throughput, low-latency security mesh providing instant packet-level visibility and autonomous exploit quarantine.
Kernel-Level eBPF Telemetry Probes
Ultra-lightweight Linux kernel probes capturing process execution, socket connections, and privilege escalation with zero CPU overhead.
Distributed ClickHouse Analytics Stream
Columnar time-series store querying billions of security events with sub-second analytical response times.
Behavioral Threat Graph Engine
Graph neural network detecting lateral network traversal, credential stuffing, and unusual API token abuse in real-time.
Autonomous SOAR Remediation Orchestrator
Automated playbook execution isolating compromised pods, revoking IAM credentials, and generating cryptographically signed forensic snapshots in <4 minutes.
Technology Stack & Infrastructure
AegisSOC neutralized a sophisticated API credential stuffing attack within seconds of probe onset. Their automated response playbooks saved us from a multi-million dollar breach.
Ready to Architect Your Enterprise Solution?
Receive an architectural review and candidate squad shortlist within 24 hours under complete NDA protection.
Schedule Architecture Review↗